Security
No certification claimed until it is audited
An independent code review of v1.0 is complete. Certification comes only after an independent audit.
Assurance roadmap
What is reviewed, planned and targeted
- Independent code review of v1.0 completed in November 2026; its findings were fixed or scheduled for v1.1 with interim controls in the runbook.
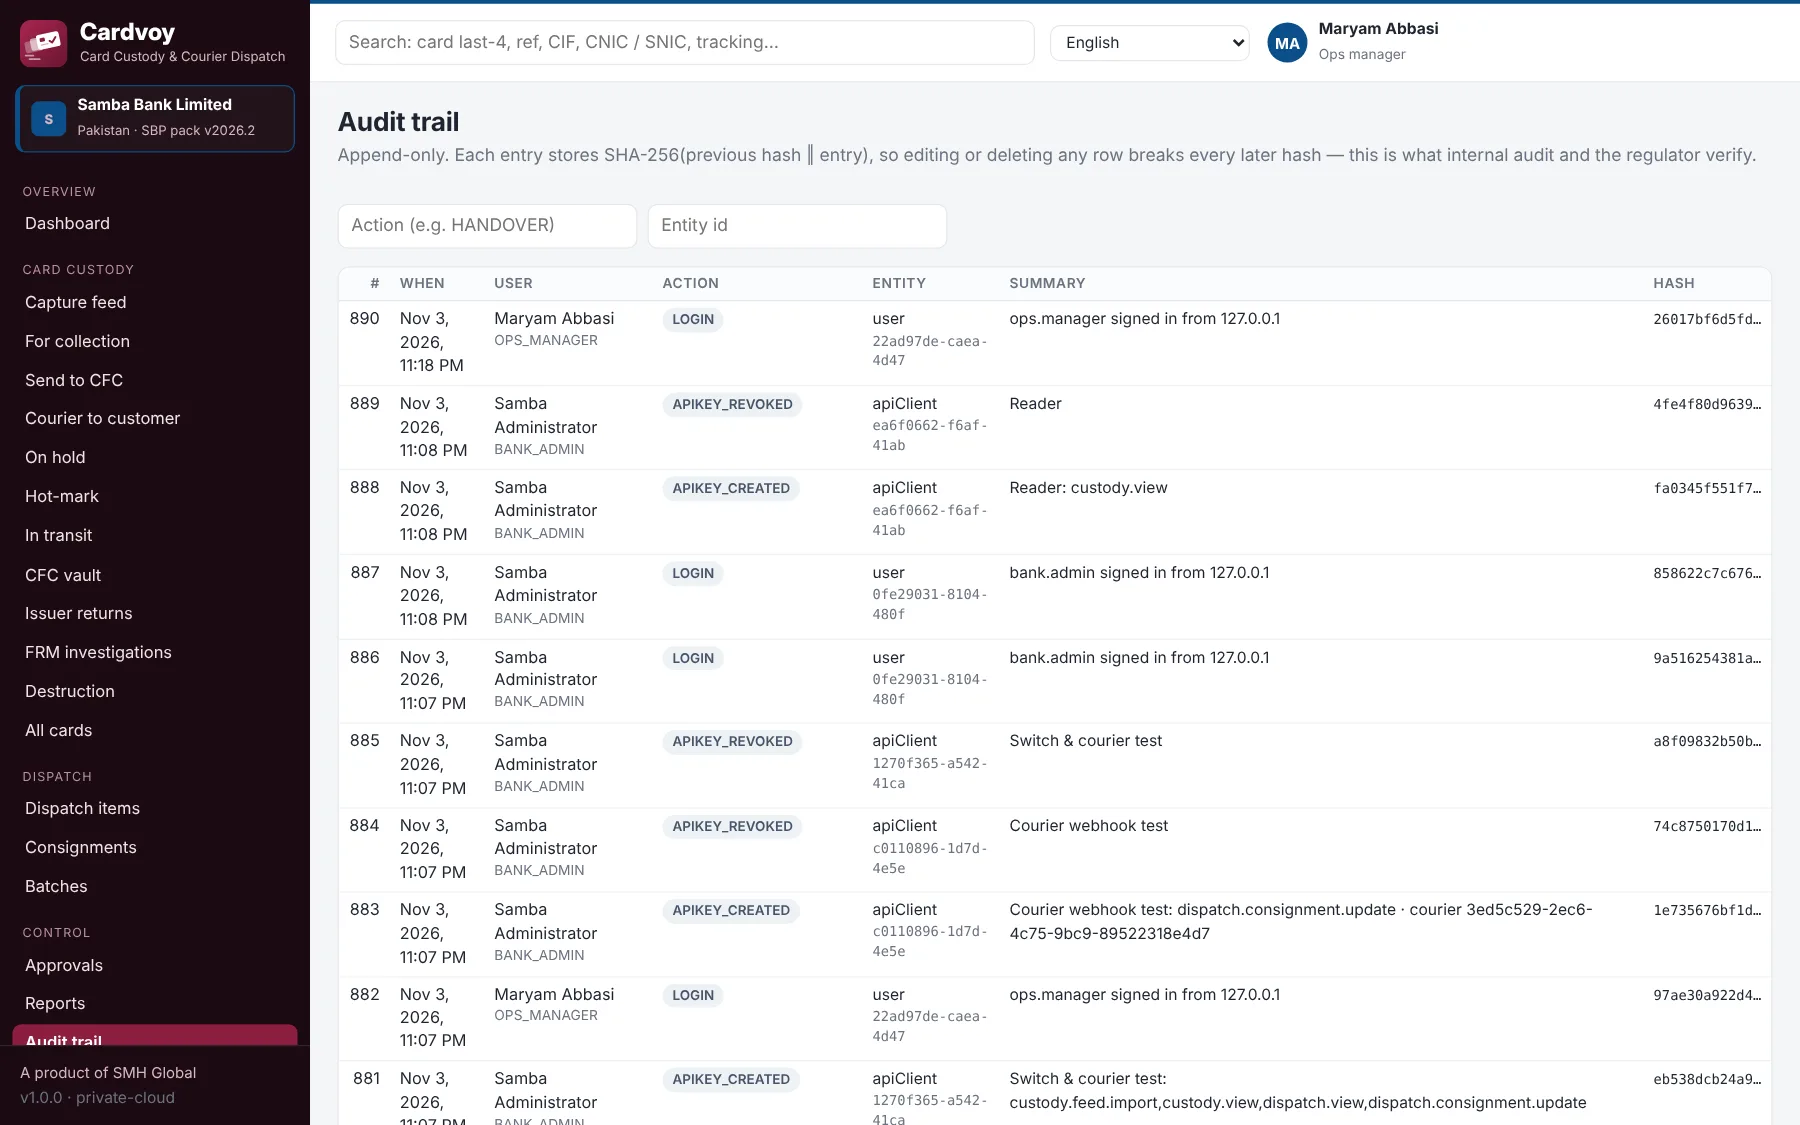
- Database row-level security, a least-privilege database role and externally anchored audit hashes on write-once storage (v1.1).
- Independent penetration test before the first production go-live.
- Control mapping to PCI DSS and ISO/IEC 27001 (v1.2). Cardvoy is designed to reduce the bank's card data scope; no certification is claimed.
Reporting a vulnerability
Write to info@smhglobal.com.pk with the subject "Security". Please do not test against bank environments. We acknowledge reports within two working days and keep you informed until the issue is fixed.
See Cardvoy with your own process.
Book a walkthrough: we set up your branches, card centre, couriers and country pack in a private proof of concept and follow a captured card from the ATM to the customer.