Standards and compliance
Designed around what regulators and auditors ask for
Cardvoy does not make a bank compliant on its own. It gives the bank controls, deadlines and evidence that map to the rules it must follow, and shows where each one comes from. Mapping is not certification.
Regulatory requirements and how Cardvoy supports them
| Requirement | Market | In Cardvoy |
|---|---|---|
| Captured on-us card collectable at the branch for a minimum period | PK | Pack floor of 5 working days; SLA clock on the pack calendar |
| Off-us captured card sent to the issuer the same day; issuer return within 2 days | PK | Routing rules and deadlines; issuer return workflow |
| Off-us captured cards destroyed by the acquirer and the issuer informed | BD | Destroy-and-notify route with issuer notice |
| Card records kept for 10 years | PK | Retention floor in the pack; long-term backups in the AWS package |
| Cards delivered only to the named customer or an authorised person | SA and all | One-time code, ID match and signature at handover; authorised-representative rules |
| Dual control and an audit trail for card destruction | All | Locked maker-checker, two witnesses, numbered certificates |
| Customer data residency and cloud outsourcing rules | AE, QA, SA, all | Deployment in-country, in a private cloud or on premises |
| Complaint statistics and captured-card registers | All | Regulator reports per country pack |
Standards and rules
| Family | Standards and rules | What Cardvoy provides |
|---|---|---|
| Regulators | State Bank of Pakistan; Bangladesh Bank; Saudi Central Bank; Central Bank of the UAE; Central Bank of Bahrain; Central Bank of Kuwait; Central Bank of Oman; Qatar Central Bank | Deadlines, destruction rules, record retention, identity documents and returns in each country pack, with the circular and clause behind every limit. |
| Payment card security | PCI DSS v4.0.1; PCI PIN Security | Card numbers tokenised and encrypted, masked on screen, full number only under dual control; PIN mailers never travel with their cards. Cardvoy reduces the bank's card data scope; it is not itself certified. |
| Information security | ISO/IEC 27001:2022; NIST CSF 2.0; OWASP ASVS 5.0 | Role-based access, maker-checker, logging, change control, supplier controls for couriers, input validation, security headers and rate limits. |
| Internal control and audit | COSO; IIA Global Internal Audit Standards | Segregation of duties, dual custody, witnessed destruction, hash-chained audit trail, registers and certificates. |
| Data protection | Saudi PDPL (SDAIA); UAE federal data protection law; Qatar Law 13 of 2016; Bahrain PDPL; Bangladesh Personal Data Protection Ordinance 2025 | Data residency per bank, masking, retention per country pack, deployment in-country where required. |
| The bank's own policies | Card custody and destruction; Outsourcing and courier management; Records retention; Delegation of authority | The organisation layer maps each policy to a configured control, inside the limits the country pack allows. |
Links go to the publishers' official pages. Names belong to their owners; Cardvoy is not affiliated with or endorsed by any of them.
Country rules live in country packs
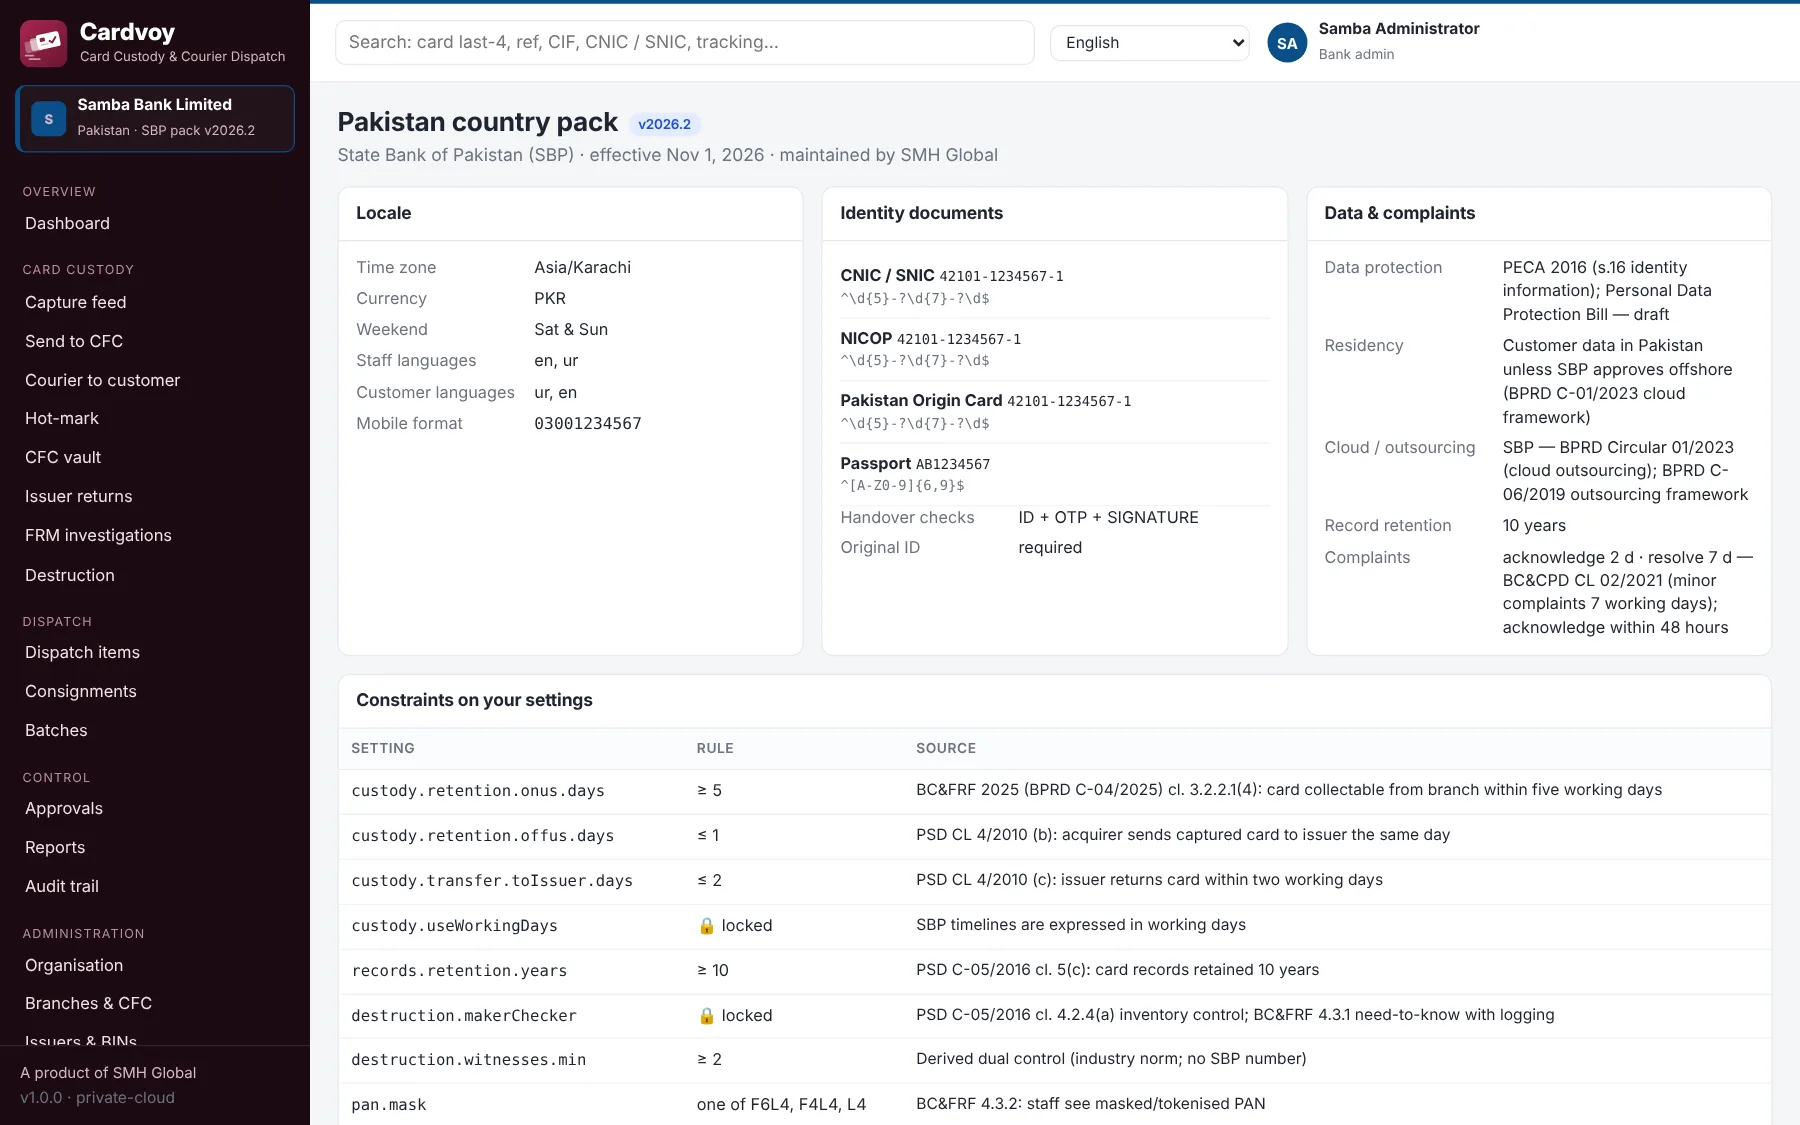
Each country pack lists the regulator documents it implements, and the configuration screen shows every constraint with its reference. A new circular becomes a pack version that SMH publishes to every bank at once.
See Cardvoy with your own process.
Book a walkthrough: we set up your branches, card centre, couriers and country pack in a private proof of concept and follow a captured card from the ATM to the customer.